Centralized SSO Server
Categorie
Description
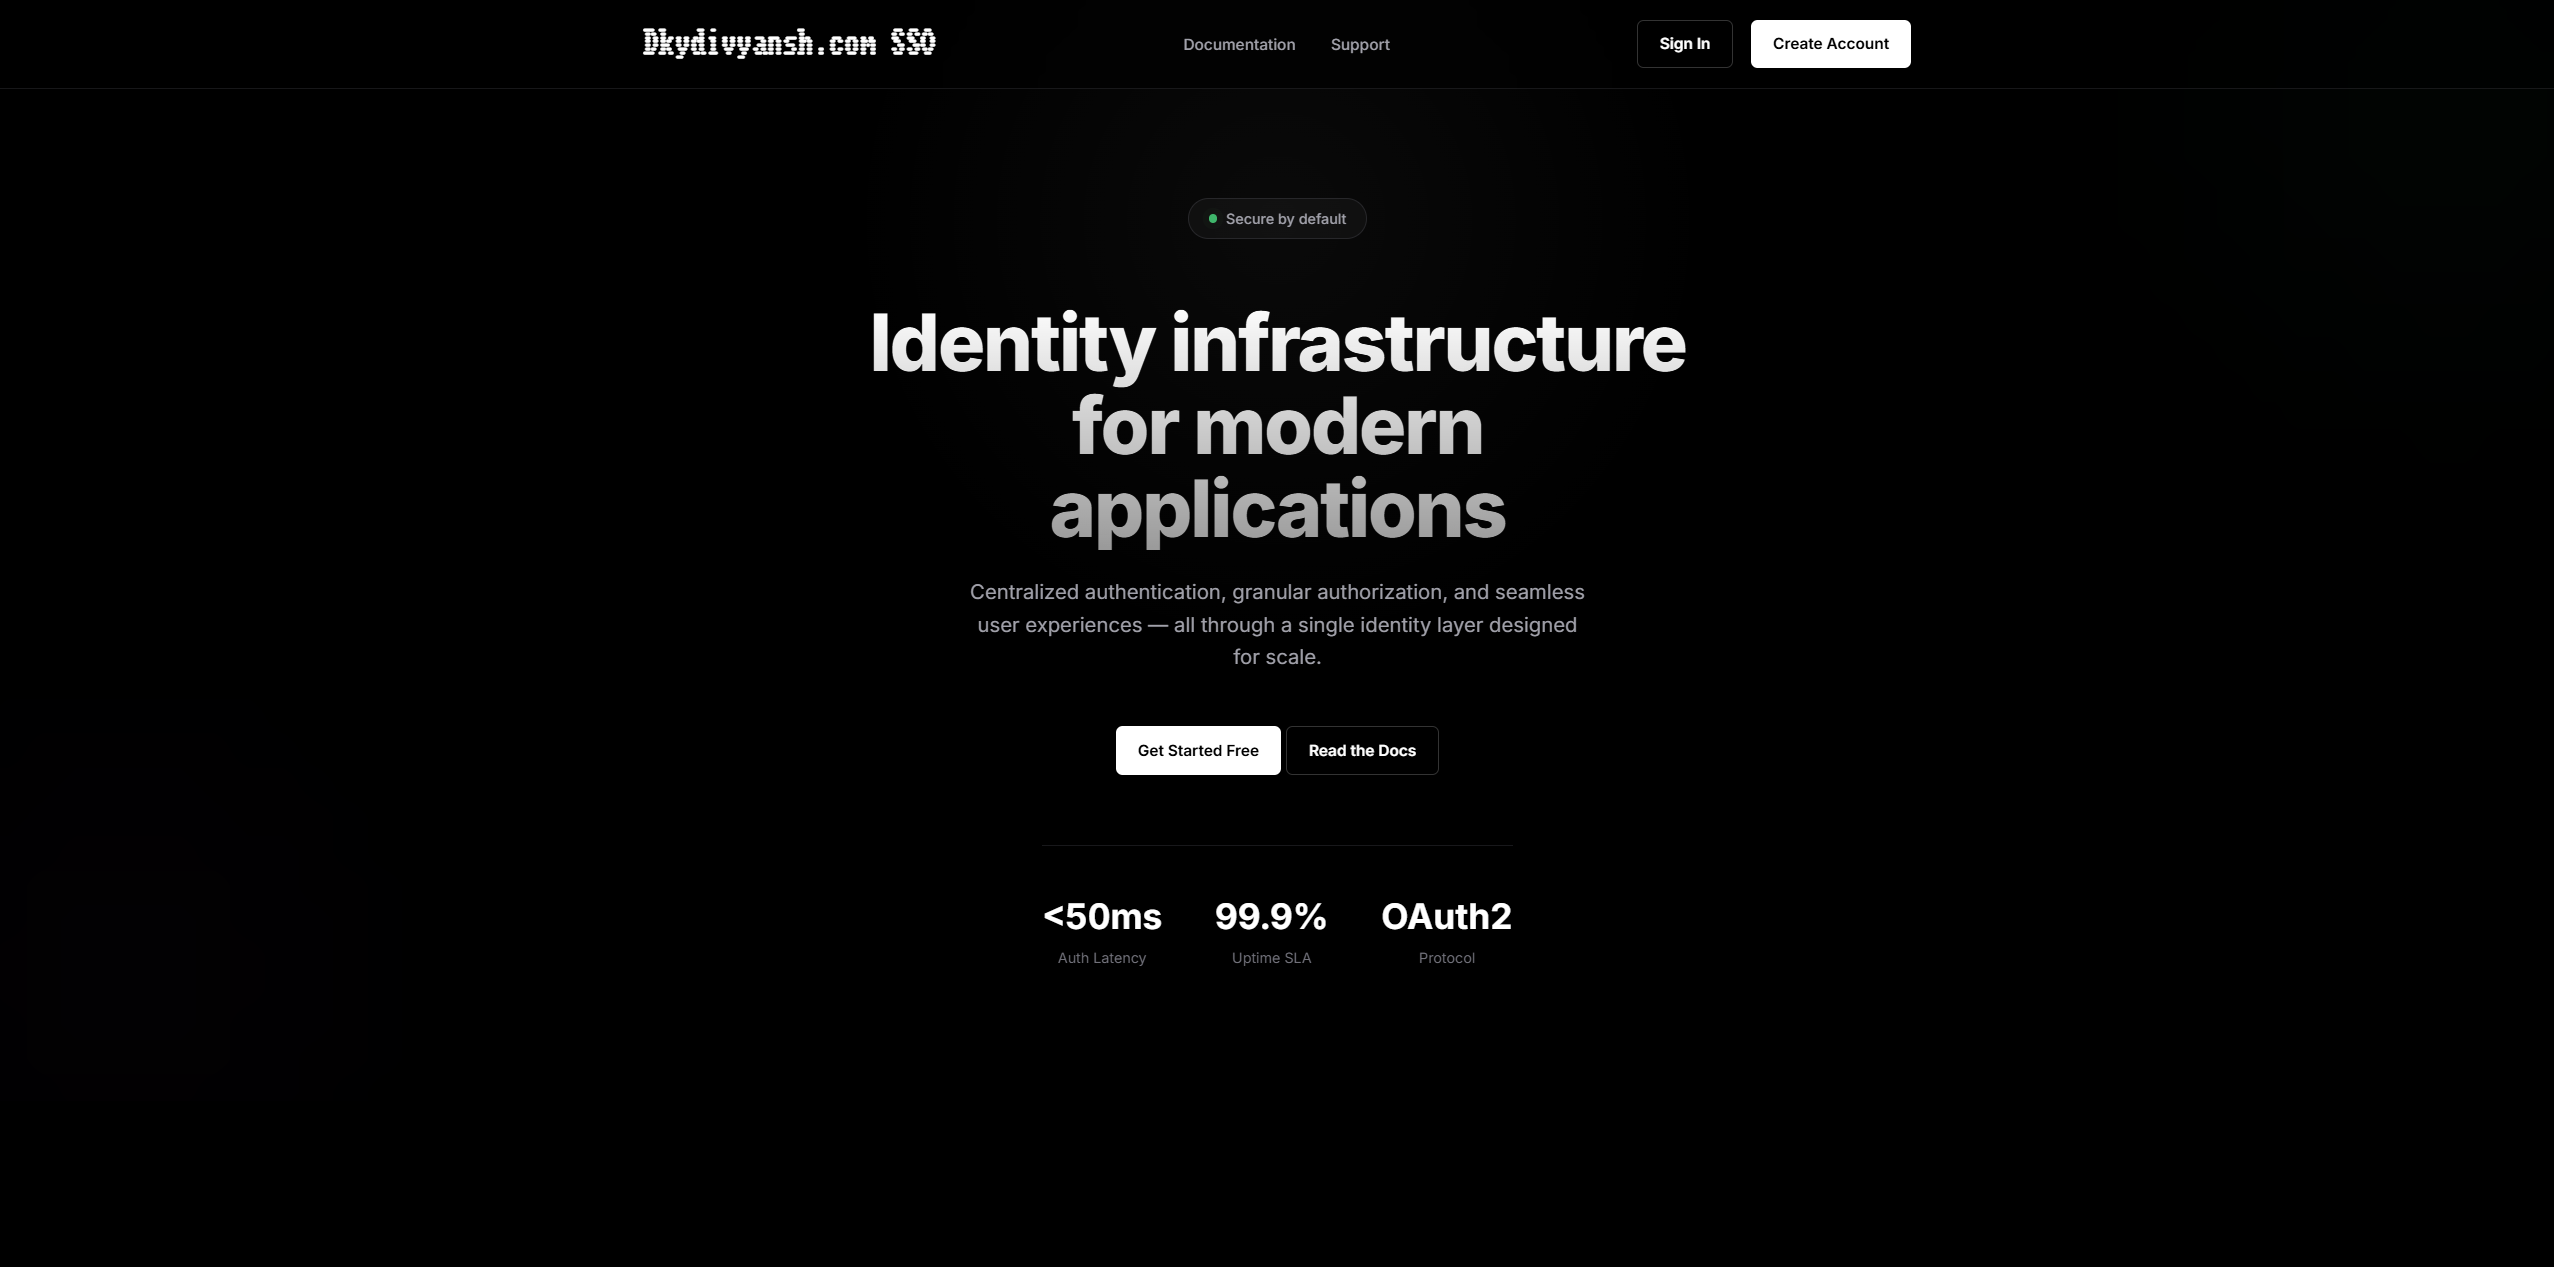
Its is a production-grade authentication and authorization infrastructure designed to serve as a single identity layer across multiple applications.
Core Authentication
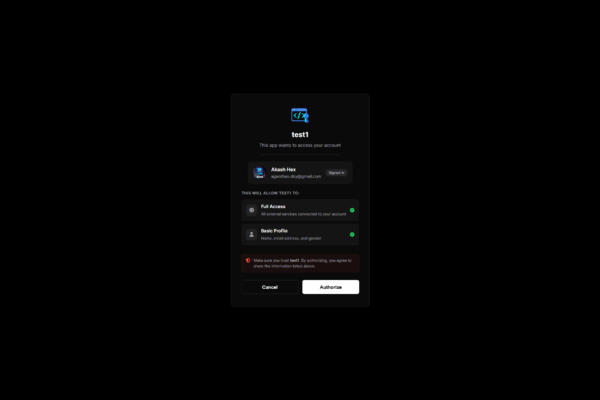
- OAuth 2.0 Authorization Code Grant flow with PKCE-ready architecture
- JWT-based stateless session management with hybrid server-side tracking
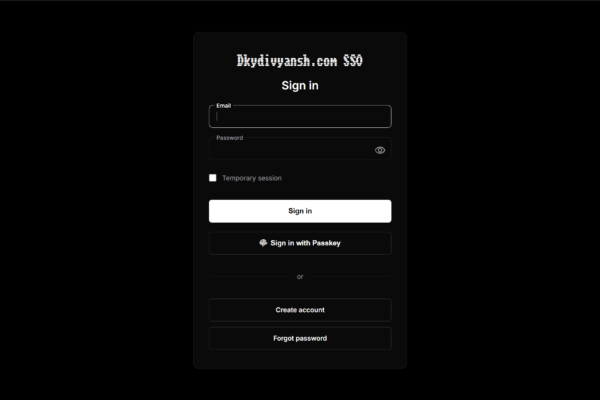
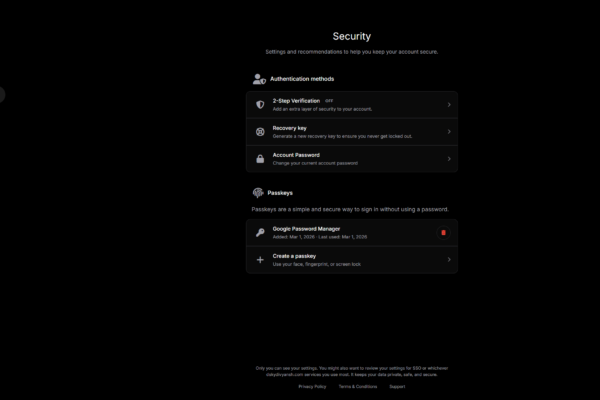
- WebAuthn/FIDO2 passwordless authentication (passkeys)
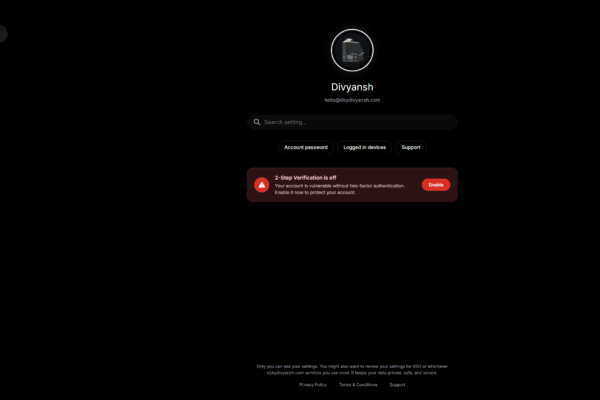
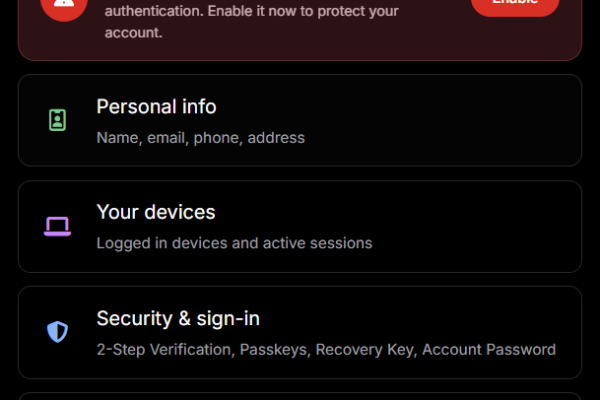
- TOTP-based Two-Factor Authentication with recovery keys
- Secure password hashing (bcrypt), email-verified registration, and OTP-based password reset
Developer Portal & API
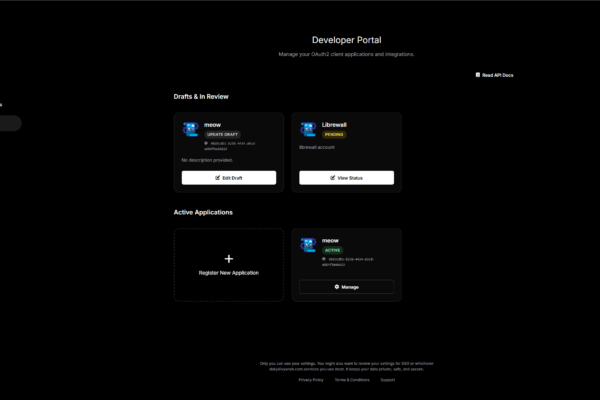
- Self-service developer console for registering OAuth clients
- Draft-based application review workflow with admin approval
- RESTful API endpoints:
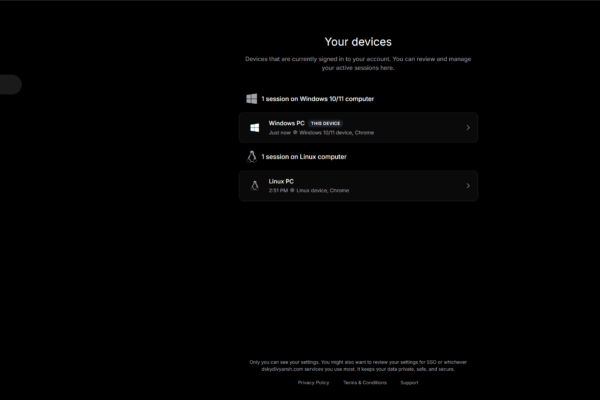
/api/authorize,/api/token,/api/userinfo,/api/revoke - Scoped access control (basic, internal, extended) with granular user consent management
Admin Panel
- User management (search, disable/enable accounts)
- Account deletion request review with full data purge
- OAuth client draft approval/rejection with email notifications
Tech Stack: PHP 8 · MySQL/MariaDB · JWT (RS256) · OAuth 2.0 · WebAuthn/FIDO2 · TOTP (RFC 6238) · bcrypt · cURL-based email API · Vanilla JS · CSS3 with custom design system
Infrastructure: Custom MVC router · Role-based access control (member/developer/admin) · Post/Redirect/Get pattern · CSRF protection · Secure session handling · SEO-optimized landing page with responsive design
Explore More
Explore More
Explore More
Explore More
PCB Badge
PCB Badge

BareMetal.js
BareMetal.js
E2EE Chat Terminal – Onion Service
E2EE Chat Terminal – Onion Service

ESP32 RF Spectrum Scanner & Sonifier
ESP32 RF Spectrum Scanner & Sonifier

Creative Shop (e-commerce)